Tech
New AI cybercrime tool breaches banking KYC systems using advanced deepfake technology

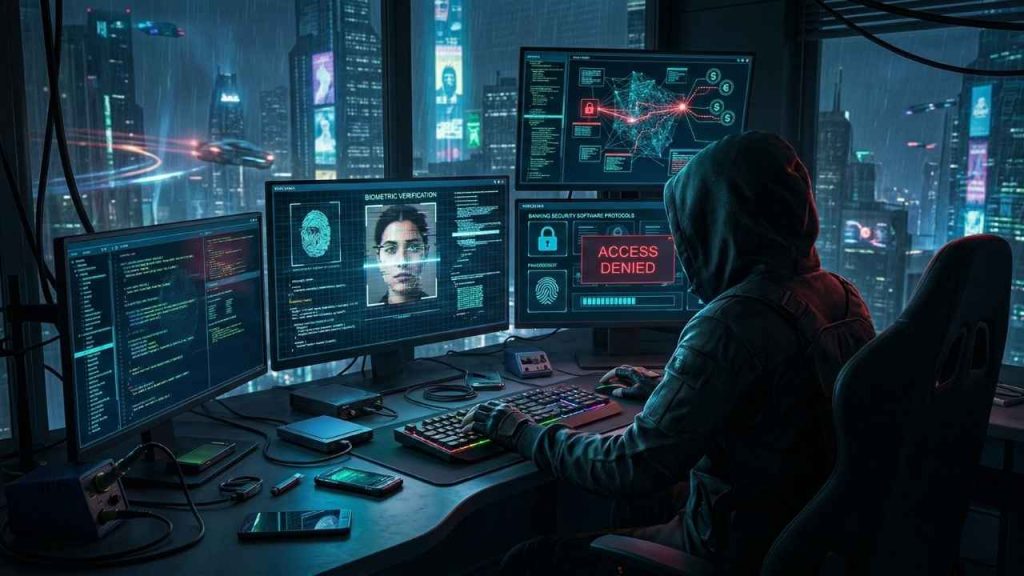
According to data published by Dark Web Informer, the actor Jinkusu is marketing an AI cybercrime tool capable of compromising security in 200,000 fraud cases via deepfakes. This fraudulent kit allows bypassing identity verification protocols on financial platforms, marking a critical turning point in protecting today’s global digital assets efficiently.
The system employs cutting-edge technology to perform real-time face swaps with alarming precision and speed. By integrating tools such as InsightFace, attackers achieve fluid gesture transfers that effectively deceive traditional biometrics in real-time. Since these methods evolve rapidly, trust in remote identification processes is currently under an unprecedented technical threat within the global financial infrastructure.
Jinkusu’s sophistication redefines global synthetic identity fraud
Unlike conventional impersonation methods, Jinkusu utilizes sophisticated voice modulation algorithms to personify legitimate users. This capability allows cybercriminals to bypass auditory security layers in banking institutions, generating a structural vulnerability in modern financial systems today. Despite regulatory efforts, the accessibility of these tools democratizes organized crime on a massive and dangerous scale.
Deddy Lavid, an executive at a leading platform in the blockchain sector, warns about the ecosystem’s systemic shortcomings. The expert points out that artificial intelligence drastically lowers barriers to synthetic identity fraud, making the platforms’ front doors a critical failure point. Therefore, it is imperative to adopt a layered security approach that combines verification with proactive monitoring.
Technical analysis performed by Vecert Analyzer reveals a worrying tactical transition compared to previous cycles. While 2022 attacks focused on basic phishing, in 2026 we observe a complete automation of social engineering through deep neural networks globally. This metamorphosis of the attack vector suggests that static defense methods have become obsolete against these dynamic adversaries.
How does artificial intelligence alter the current cryptographic security landscape?
Investors faced historical losses worth 5.5 billion dollars during the last fiscal year alone. These data, linked to psychological manipulation schemes, demonstrate the lethal effectiveness of combining social engineering and technology advanced artificial. Since the software does not require deep technical knowledge, the volume of potential attacks could scale exponentially during the current financial economic cycle.
The same actor, Jinkusu, has been previously linked to the launch of the dangerous Starkiller phishing kit. This malware uses a headless Chrome browser inside a Docker container, allowing to intercept credentials through a real-time reverse proxy invisibly. Although total losses from traditional attacks recently decreased, AI cybercrime keeps the alert level at maximum throughout the global markets.
The evolution of these AI cybercrime tools suggests that visual validation no longer guarantees authenticity. The use of reverse proxies and automated browsers allows attackers to replicate legitimate sessions with fidelity that current firewalls cannot detect. However, cybersecurity companies are already working on AI-based anomaly detection models to counter this growing criminal trend.
The future of security in the cryptographic environment will depend exclusively on the integration of autonomous defenses. Platforms must implement systems that not only verify the static image but also analyze behavioral patterns and network metadata suspiciously and continuously. Proactive surveillance and the constant updating of biometric detection engines will be the pillars of digital resistance moving forward.
The post New AI cybercrime tool breaches banking KYC systems using advanced deepfake technology appeared first on The Cryptocurrency Post.

NEAR has added a new job posting to its Agent Market for a Local Services Quote Agent, an AI agent designed to contact local providers, collect responses and return side-by-side comparisons of price and availability.
The listing appeared on the official NEAR DevHub channel and was also amplified by the project’s official social accounts. According to the post, the builder who takes on the job would keep ownership of the agent and retain the revenue it generates.
The job description frames the agent as a tool for gathering real quotes from local services rather than a general chatbot. It would reach out to providers, log the replies and organize the results so users can compare options more easily.
Builder-owned agents remain central to the marketplace pitch
NEAR has positioned the Agent Market around the idea that developers can publish agents, set their terms and keep ownership after the job closes. In the official posts, the company said builders keep the agent and can earn when it is hired.
The job board format also suggests a more structured approach to AI agent development, with specific tasks posted for builders to bid on. In this case, the task centers on a practical consumer workflow: collecting quotes from local providers and presenting them in a usable format.
NEAR did not say when the Local Services Quote Agent will be completed or who will take the job. The posting does, however, show that the Agent Market is actively listing new work and pushing the marketplace model as part of its product rollout.
The post NEAR launches Agent Market job board for local services quote agent appeared first on The Cryptocurrency Post.
Monad said it has reached 1 billion transactions on its network, a milestone the project highlighted in an official post on X. The timeframe attached to the claim — 11 months — is part of the headline circulating with the update, but the post itself does not clearly spell out that period.
we really got 1 billion transactions on testnet before GTA 6 pic.twitter.com/bYrCHovN6i
— Monad (@monad) April 18, 2025
The figure points to activity on Monad’s testnet rather than mainnet. That distinction matters: a testnet can show developer and user engagement, but it does not by itself prove production usage or commercial adoption.
Monad has used recent public appearances and posts to emphasize network activity and developer interest around its ecosystem. Still, the transaction total should be read as a project-reported milestone, not as evidence on its own of demand, revenue or sustained onchain usage.
For readers following the chain, the main takeaway is narrow but concrete: Monad is claiming a large transaction count on its test environment, and the project is presenting it as a sign of momentum. The post does not provide additional breakdowns in the headline claim, such as the mix of user transactions, automated activity or the exact measurement method behind the total.
The post Monad reports 1B transactions in 11 months appeared first on The Cryptocurrency Post.
Aptos said its Encrypted Mempool is now live on mainnet, giving users the option to encrypt transaction details before block ordering is finalized. The company said the feature is designed to reduce maximal extractable value, or MEV, which can include practices such as front-running and sandwich attacks.
In an official blog post, Aptos described the rollout as an opt-in feature at the transaction level. The network said the payload is encrypted on the client side, ordered while still encrypted, and only decrypted by validators after block finalization.
The company’s official account and Aptos Labs also confirmed the mainnet launch on X, with the Labs post adding that encryption happens before submission and that decryption takes place only after block ordering is complete. That sequence is intended to keep transaction contents hidden during the period when they could otherwise be observed and used for MEV extraction.
Opt-in design keeps the feature at the transaction level
Aptos framed the launch as a user choice rather than a default network setting. According to the company, Encrypted Mempool can be enabled per transaction, allowing users to decide when they want that added layer of protection.
The mainnet launch means the feature is no longer just a technical concept or test-stage mechanism. It is now part of the live Aptos network, with the practical effect depending on whether users choose to activate it for individual transactions.
The post Aptos brings Encrypted Mempool to mainnet in move aimed at lowering MEV risk appeared first on The Cryptocurrency Post.

NEAR launches Agent Market job board for local services quote agent

Monad reports 1B transactions in 11 months

Aptos brings Encrypted Mempool to mainnet in move aimed at lowering MEV risk

RWA WEEK Singapore Announces New Wave of Institutional Speakers as October Event Draws Closer

Bittensor SN10 Work Tied to Pareto AI and Engy AI at Exploit Summit

BNB Chain Agent Studio v4 adds NodeOpsHQ for prompt-to-agent deployment

Cardalonia Aiming To Become The Biggest Metaverse Project On Cardano

P2P2C BREAKTHROUGH CREATES A CONNECTION BETWEEN ETM TOKEN AND THE SUPER PROFITABLE MARKET

WOM Protocol partners with CoinPayments, the world’s largest cryptocurrency payments processor

ETHERSMART DEVELOPER’S VISION MADE FINTECH COMPANY BECOME DUBAI’S TOP DIGITAL BANK

Project Quantum – Decentralised AAA Gaming

WOM Protocol Recommended by Premier Crypto Analyst as only full featured project for August
-
 Crypto4 years ago
Cardalonia Aiming To Become The Biggest Metaverse Project On Cardano
-
 Press Release6 years ago
P2P2C BREAKTHROUGH CREATES A CONNECTION BETWEEN ETM TOKEN AND THE SUPER PROFITABLE MARKET
-
 Blockchain6 years ago
WOM Protocol partners with CoinPayments, the world’s largest cryptocurrency payments processor
-
 Press Release6 years ago
ETHERSMART DEVELOPER’S VISION MADE FINTECH COMPANY BECOME DUBAI’S TOP DIGITAL BANK
-
 Press Release5 years ago
Project Quantum – Decentralised AAA Gaming
-
 Blockchain6 years ago
WOM Protocol Recommended by Premier Crypto Analyst as only full featured project for August
-
 Press Release6 years ago
ETHERSMART DEVELOPER’S VISION MADE FINTECH COMPANY BECOME DUBAI’S TOP DIGITAL BANK
-
 Blockchain6 years ago
1.5 Times More Bitcoin is purchased by Grayscale Than Daily Mined Coins